Okay, so check this out—I’ve carried hardware wallets in my backpack, my pocket, and once even taped to a laptop when I was being careless. Wow! You get the point: custody is messy. My instinct said that smart cards could be the neat middle ground between convenience and ironclad security. Initially I thought plastic chips were a gimmick, but then I started actually using one and things shifted.
Really? Yes. The first time I tapped a smart card to authorize a transaction, it felt like the future. Medium-length sentences here help explain why: smart cards store private keys on a secure element, isolated from the phone or computer they pair with, which reduces exposure to malware. On one hand, the card is simple. On the other hand, the cryptography inside is complex and robust, though actually you don’t need to be a crypto nerd to use it.
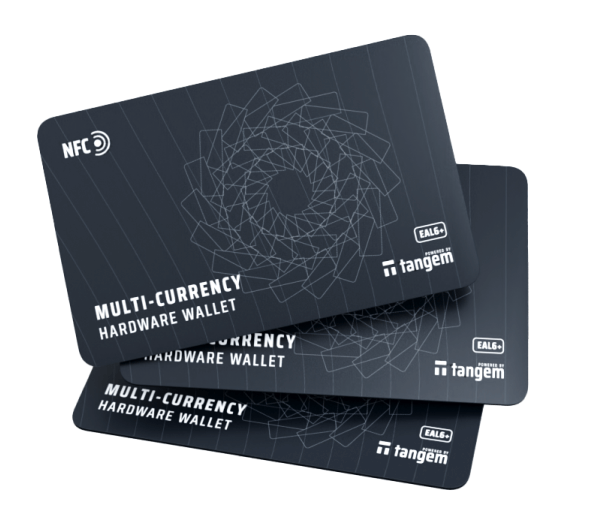
Here’s the thing. Smart-card wallets sit between custodial apps and bulky hardware devices. Hmm… That hit me when I was teaching friends how to move funds—some wanted easy, some wanted safe, and most wanted neither complicated instructions nor metal bricks. They’re basically a contactless chip that signs transactions without ever spilling the private key. My first impression was skepticism, but using one changed my view—fast.
Let’s be honest: user habits are weak. People reuse passwords. They click on sketchy links. They download browser extensions without reading permissions. Seriously? Yes. So whatever security model you pick, it must work with human laziness and curiosity. A smart-card wallet often wins here because it blends a physical possession factor with simple UX. It forces a tap, a presence check, which reduces automated exploitation.
At a technical level, smart cards implement secure elements—tamper-resistant chips that execute cryptographic operations internally. Whoa! Those chips hold private keys and never export them, not even to devices you trust. That means even if your phone is totally pwned, the key remains locked away. Initially I thought that was overkill for casual users, but then I realized most breaches come from endpoints, not from the crypto math itself.
On one hand, smart cards bring portability and low-profile design that looks normal in your wallet. On the other hand, they sometimes lack the screen feedback that hardware “brick” wallets provide, which can make transaction confirmation less intuitive. Actually, wait—let me rephrase that: some smart cards pair with companion apps that show transaction details, and a careful implementation will display critical info before signing. But many cheap setups skip that step, and that, that part bugs me.
I’m biased, but I’ve used a Tangem-style approach and liked how it streamlines recovery. Hmm… My brain still compares seed phrases with plastic cards. Seed phrases are powerful, but they demand education and safe offline storage. A smart card often marries a one-tap experience with a recovery mechanism that’s a lot less scary for average people, though the trade-offs matter. If you lose a single smart card, recovery depends on how the provider designed the backup system.
Here’s where design choices matter most. Some smart-card wallets let you create multiple cards that are part of a multi-signature scheme, which is neat because it spreads risk across physical items. Whoa! Multi-sig on plastic is surprisingly approachable if the UX is done right. Other cards lean into custodial backup, which I don’t love. My working rule: assume hardware can be lost, stolen, or damaged, and build a recovery you understand before you need it.
Let me walk through a practical scenario. You hold a smart card with your keys. To send funds, you tap or scan the card using your phone’s NFC and confirm the operation in a companion app. Really? Yes, that’s usually it. The private key never leaves the chip; the card signs the transaction. If the phone is compromised, it can display a forged balance or fake history, but it cannot extract the signing key without physical access to the secure element.
There are vulnerabilities though. Side-channel attacks, advanced fault injection, or sophisticated supply-chain tampering can target secure elements, especially if a device is poorly validated. Hmm… My gut says these attacks are rare for everyday users, but they matter for high-value holdings. On a practical level, verify provenance and buy from reputable vendors. For example, reputable smart-card products like the ones described at tangem hardware wallet publish details on security audits and manufacturing processes, which is the sort of transparency you want.
One stumbling block is interoperability. Different blockchains and token standards have different signing requirements, and not every card supports every chain natively. Whoa! That forces users into a bit of ecosystem thinking. Initially I thought “one card to rule them all” was realistic. But in practice, you might need a card that supports Ethereum, Solana, or Bitcoin in distinct ways, and some ecosystems require additional app layers on the companion device.
Let me be frank about trade-offs. Portability and UX often come at the cost of the richest security features. Long-time crypto holders who want maximum assurance favor air-gapped, open-source hardware with screens and verification. Short-term adopters prioritize simplicity. On the flip side, people who carry only a mobile device face phishing and remote hacking—so a physical card still offers a meaningful security layer. My experience shows the middle ground—smart cards—can be the best compromise for many.
Something felt off about recovery models. I once helped a friend recover from a lost device and it was messy. He had a single backup card, but had no secondary plan. That was my wake-up call. You should design for loss like you design for failure: assume it will happen and practice the steps. That means creating multiple recoverable components, recording clear instructions, and verifying that your recovery plan works before you need it. Somethin’ as trivial as a laminated instruction card can save hours of panic.
Security practices that actually stick are the ones that fit real lives. For instance, a simple habit: always check the last four characters of the signing key or the transaction summary before approving. Short reminder. It helps avoid rushed confirmations. On the other hand, too many verification steps will break adoption. So there’s a balance: enough checks to stop simple theft, but not so many that people ignore them.
Here’s a quick technical checklist I use when evaluating smart-card wallets. 1) Is the secure element certified (Common Criteria, CC EAL, or similar)? 2) Are the firmware and manufacturing processes auditable or at least transparent? 3) Is there documented resistance to side-channel and fault-injection attacks? 4) How does recovery work and are backups user-friendly without being central points of failure? 5) Does the product support the chains you care about? Each item matters, though priorities differ by threat model.
For everyday users, the main wins are convenience and reduced attack surface. Wow! You tap, you confirm, you go on with your life. For power users, the wins are in modular designs that allow multi-sig or complexity, though that increases setup friction. My takeaway is that smart cards belong in a layered-security approach: they are neither an all-powerful cure nor a mere toy. They are a pragmatic, human-friendly tool you can reasonably trust.
Okay, so what’s my recommendation if you’re shopping? First, think about your threat model. Are you safeguarding retirement funds, or just dabbling in altcoins? Second, buy from a vendor that publishes security documentation and offers a sensible recovery path. Third, practice your recovery—don’t just assume it will work. And finally, don’t stash everything in one place; diversification of custody is a simple, useful habit.
Final thoughts
I’m not 100% sure anything is perfect. Still, smart-card wallets solve many UX-security problems that plague mainstream crypto adoption. Really. They reduce key-exposure, feel familiar to people who carry plastic cards, and integrate with phones without handing over control. That mix matters if you want widespread adoption and sane security practices.
On the flip side, don’t ignore the details—manufacturing, audits, recovery, and chain support. Initially I thought physical possession alone was enough, but experience showed me that the real work is in the surrounding processes. So practice, verify, and treat your smart card like a passport: valuable, personal, and replaceable only with planned steps.
Common Questions
Can a smart-card wallet be hacked remotely?
Short answer: not directly. The private key stays on the chip, which means a remote app or compromised phone can’t extract it. Long answer: remote attackers can try to trick you into signing malicious transactions via social engineering or fake UIs, so verify transaction details and use reputable companion apps.
What happens if I lose the card?
It depends. Some systems allow multiple cards or recovery seeds; others let you reissue via a documented recovery process. Practice your recovery plan. Seriously, test it once in a low-stakes scenario so you know what to expect when it matters.
Are smart-card wallets suitable for long-term storage?
Yes, when combined with a robust recovery and physical security measures. They’re a strong option for long-term custody if the card uses a certified secure element and you maintain backups in separate, secure locations.